Category Archives: Things that are bad

New restrictions for Windows 10 Pro version

When it became clear that Microsoft intended Windows 10 to be an advertising platform, I wondered how they would sell it to business and education customers (see my Windows 10 review). I doubted that anyone would allow Windows 10 into the workplace unless the advertising and related privacy-compromising instrumentation could be disabled.

It wasn’t long before we started seeing tools and techniques for turning off these undesirable features, and Microsoft even provided some of their own, in the form of Group Policy settings.

The Group Policy editor is included with all versions of Windows 10 except Home. It makes the job of managing Windows settings easier for system administrators, since the alternative is editing the Windows registry.

So the answer to my question about disabling unwanted Windows 10 features for business customers would be Group Policy. Which is okay, but doesn’t help anyone using the Home version. Which is one reason why I tell people to avoid Windows 10 Home. Unless you’re on a tight budget, and don’t mind seeing advertising in your O/S, Windows 10 Professional is highly recommended for personal use.

So: get Windows 10 Pro, disable all the unwanted advertising and privacy-related settings, and you’re good to go, right? Not so fast.

The folks over at GHacks recently confirmed that Microsoft will lock down Group Policy in the Pro version of Windows 10 with the upcoming anniversary update. Many of the more annoying features will still have visible settings in the Group Policy editor, but changing them will have no effect. Even changing the corresponding settings in the registry apparently won’t work.

Microsoft’s message to the world seems to be “Okay, you don’t want us to advertise and track your users in Windows 10 in the workplace, so we’ll give you some tools to turn those features off. But we’ll be damned if we’ll let anyone else (i.e. Home and Pro users) turn that stuff off.”

To which my response is: “Dear Microsoft: Screw you. I won’t buy Windows 10. I won’t use Windows 10. I will tell anyone who cares to listen that they should avoid Windows 10 like they would Ebola. I will use Windows 7 and 8.1 until you abandon them, and then switch to Linux.”

There’s more over at BetaNews.
Ransomware update

Ransomware has been in the news a lot lately. The CryptXXX ransomware is no longer susceptible to easy decryption, and it’s been making a lot of money for its purveryors, in many cases using compromised, high profile business web sites as its delivery mechanism. On a more positive note, the people who created the TeslaCrypt ransomware stopped production and released global decryption keys. New ransomware delivery systems are able to bypass Microsoft’s EMET security software. The Cerber ransomware was recently delivered to a large proportion of Office 365 users via a Word document in an email attachment. And an even more hideous piece of malware surfaced in the last week: posing as ransomware, Ranscam actually just deletes all your files.

Ransomware is different from other kinds of attacks because of the potential damage. It can render all your data permanently inaccessible. Even paying the ransom is no guarantee that you will get all your data back intact. Other types of attacks typically try to fly more under the radar: trojans and rootkits want to control and use your computer’s resources; and viruses want to spread and open the door for other attacks. While other types of attacks can be fixed by removing the affected files, that doesn’t work for ransomware.

Like other types of attacks, ransomware first has to get onto your computer. These days, simply visiting the wrong web site can accomplish that. More common vectors are downloaded media and software, and email attachments. Preventing malware of any kind from getting onto your computer involves the kind of caution we’ve been advising for years; ransomware doesn’t change that advice.

What CAN make a big difference with a ransomware attack is limiting its reach. Once on a computer, ransomware will encrypt all data files it can access; specifically, files to which it has write access. Ransomware typically runs with the same permissions as the user who unwittingly installed it, but more insidious installs may use various techniques to increase its permissions. In any case, limiting access is the best safeguard. For example, set up your regular user so that it cannot install software or make changes to backup data.

Here’s a worst-case scenario: you run a small LAN with three computers. All your data is on those computers. Your backup data is on an external hard drive connected to one of those computers, and a copy exists on the Cloud. For convenience, you’ve configured the computers so that you can copy files between them without having to authenticate. Once ransomware gets onto one of the computers, it will encrypt all data files on that computer, but it will also encrypt data it finds on the other computers, and on the external backup drive. Worse still, some ransomware will also figure out how to get to your cloud backup and encrypt the data there as well.

How to limit your exposure? Require full authentication to access computers on your LAN. Use strong, unique passwords for all services. Store your passwords in a secure password database. Limit access to your backup resources to a special user that isn’t used for other things. In other words, exercise caution to avoid getting infected, but in case you get infected anyway, make sure that you have walls in place that limit the reach of the ransomware.

Most ransomware targets Windows systems, so most of the verbiage out there is about Windows as well. This article covers the basics fairly well.

Pre-installed crapware still a problem

A recent report from Duo Security shows that pre-assembled, ready-to-run computers purchased from major vendors almost always include pre-installed software that often makes those computers much less secure. That’s in addition to being unnecessary, unstable, resource-hungry, and often serving primarily as advertising conduits.

If you purchase a pre-assembled computer, you should uninstall all unnecessary software as soon as possible after powering it up. Before even connecting it to a network. It can be difficult to identify exactly which software should be removed, but a good starting point is to remove anything that shows the manufacturer’s name as the Publisher. PC World has a helpful guide.

And now the good news, at least for some of us: Microsoft now provides a tool that allows a user with a valid license to reinstall Windows 10 from scratch at any time. Minus all the crapware that the manufacturer originally installed.

Major vulnerabilities in Symantec security products

Earlier this week, a Google researcher published a report on vulnerabilities affecting all Symantec security products, including Norton Security, Norton 360, legacy Norton products, Symantec Endpoint Protection, Symantec Email Security, Symantec Protection Engine, and Symantec Protection for SharePoint Servers. All platforms are affected.

From the original report:

These vulnerabilities are as bad as it gets. They don’t require any user interaction, they affect the default configuration, and the software runs at the highest privilege levels possible. In certain cases on Windows, vulnerable code is even loaded into the kernel, resulting in remote kernel memory corruption.

Symantec quickly released security advisories and updates to address the vulnerabilities, including SYM16-010 and SYM16-011.

Anyone who uses Symantec or Norton security products should install the available updates as soon as possible.

Microsoft updates now harder to find

Until I hear a better explanation, I’m going to assume that Microsoft’s latest move – removing updates from its Download Center – is just another way to force user eyeballs through conduits for which they can sell advertising space.

Starting May 10, Microsoft wants you to use the Update Catalog instead of the Download Center. Previously, security bulletins included links to the Download Center, but since most updates (including security updates) will no longer be available there, those links will now point to the Update Catalog.

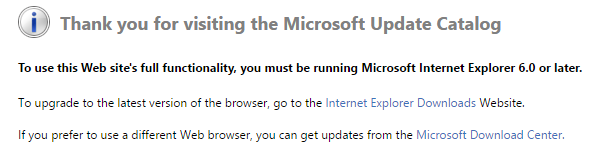
Okay, so we can use the Update Catalog, right? But guess what happens when you visit the Update Catalog with a browser that isn’t Internet Explorer? MS Update Catalog: IE Only Please

Note the final line of that message, which encourages visitors to use the Download Center instead. I guess Microsoft hasn’t gotten around to changing that. It should probably say “If you prefer to use a different Web browser, you’re out of luck.”

Most regular users get their updates via Windows Update, and won’t be affected by this change. Once again, it’s power users and system admins who will be affected the most. Does Microsoft hate us, or are they just ignoring us?

Although other mechanisms exist for obtaining updates, the Download Center was certainly convenient. Are we likely to see more third party sites offering Microsoft updates? Probably, although Microsoft frowns on this sort of thing and will probably move to shut them down.

The perils of using free services

RIP TweetDeck

Twitter is pulling the plug on the Windows version of its popular TweetDeck application, pushing users to switch to the web-based version. Although they claim otherwise, the reason is simple: web applications are easier to monetize.

Twitter purchased TweetDeck in 2011 because users found its interface much more useful than the Twitter web interface, and were switching in large numbers. This translated into a loss of advertising revenue for Twitter. There were immediate predictions that Twitter would kill off TweetDeck, and that’s finally happening.

For some users, switching to the web-based TweetDeck will not be a problem. The two interfaces are virtually identical. But having a compact, separate application has several advantages: I can configure it to start automatically with my computer; I can leave it running all the time without hurting my computer’s performance; and it’s not – like all web-based apps – inherently fragile. So I’m looking at alternatives. If I find one I like, I’ll post about it.

Mandrill email no longer free

If you use Mandrill’s email service, you should start looking for an alternative. Unless you think $20 per month seems like good value to send a few emails.

I originally started using Mandrill because my Internet Service Provider’s email service was increasingly less willing to process email from domains I host, including boot13.com. If you don’t host your own domains, and you don’t send large quantities of email, you’re unlikely to ever need a ‘transactional email’ service like Mandrill.

Luckily, there are plenty of alternatives to Mandrill. Right now I’m evaluating MailGun, which is free for up to 10,000 emails per month, and supports DKIM and SPF, technologies that help to identify legitimate senders and reduce spam.

Critical security flaw affects millions of systems

Here we go again. Researchers have discovered (actually more like rediscovered) a very bad flaw in the commonly-used GNU C Library, also known as glibc.

The flaw has existed, undiscovered, since 2008. It was discovered and reported to the glibc maintainers in July of 2015 (CVE-2015-7547), but nothing was done about it until Google researchers re-discovered the flaw and reported it on a public security blog.

The glibc maintainers reacted to the Google revelations by developing and publishing a patch. It’s not clear why such a serious vulnerability was not fixed sooner.

But that’s not the end of the story. Any computer or device that runs some flavour of Linux, including most of the world’s web servers and many routers, is potentially vulnerable. Individual software applications that are compiled with glibc are also potentially vulnerable.

Although it’s safe to assume that diligent sysadmins will update their Linux computers, tracking down all the affected software will take time. The Linux firmware running on routers and other network devices will be updated much more slowly, if at all. All of this opens up many exploitation possibilities for the foreseeable future.

The good news is that there are several mitigating factors. Many routers don’t use glibc. In some cases, default settings will prevent exploits from working. Android devices are not vulnerable. Still, this problem is likely to get worse before it gets better.

Update 2016Feb20: Dan Kaminsky just posted his analysis of the glibc vulnerability. It’s very technical, but if you’re looking for a deeper dive into this subject, it’s a great place to start. Dan helpfully explains why it’s difficult to predict just how bad things will get.